Resolve: NetSuite Patch Causing “Not Allowed” SuiteCommerce Error
NetSuite recently pushed live a security patch. Unless you apply it, your SuiteCommerce site will display “Not Allowed” permissions errors.
Read the Article
NetSuite recently pushed live a security patch. Unless you apply it, your SuiteCommerce site will display “Not Allowed” permissions errors.
Read the ArticleLearn how to grant existing NetSuite customer contacts access through CSV import, including Customer Center roles, Contact Access field mapping, and notifications.
Read the Article
Learn about the security features introduced in SuiteCommerce 2025.2.0, including CAPTCHA, email-domain blocklisting, and email verification, plus existing storefront access controls and customization options.
Read the Article
Troubleshoot the NetSuite Suitelet "You do not have privileges to view this page" error by checking script deployment permissions, the Online Form User role, and the Online Forms feature.
Read the Article
How to resolve "WARNING: This customer does not have access to a website. The subsidiary associated with the customer’s assigned web site is not online."
Read the Article
Learn workarounds to resolve an "Insufficient Permissions" error will be thrown by a user event script in NetSuite, even though its deployment is set to run as administrator.
Read the Article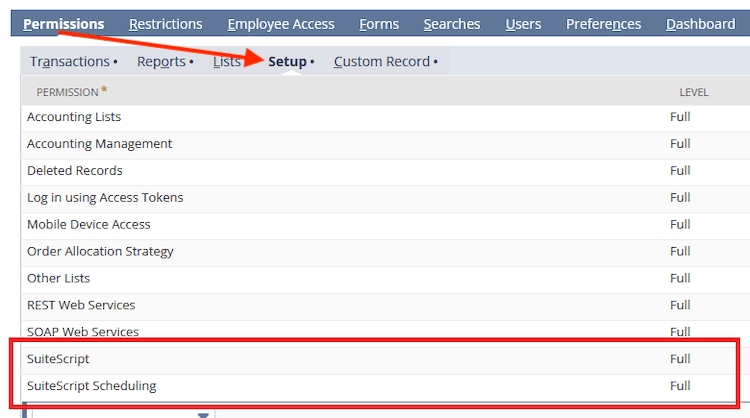
There may be a need to force all current SuiteCommerce website users to update/reset their passwords. Thankfully, there is a way to do this in bulk.
Read the Article
SOX compliance for NetSuite starts with a two-tiered review of your systems and controls. First is the ‘Management’ audit: Section 404(a). 404(a) is an annual evaluation of a company’s internal controls over financial reporting (ICOFR). It should involve a thorough review and risk assessment of your processes around financial data and financial reporting. The goal is to identify where controls are needed to mitigate risk. If that wasn’t fun enough, 404(a) is only the precursor to the full external audit required by Section 404(b). This is where your external auditors will come in and ask: have the risks identified in Section 404(a) been mitigated? Have any risks been overlooked?
Read the Article
One of our clients was facing an audit by a government agency and needed us to create a status change detection solution on a tight deadline. Here's how we did it.
Read the Article
One of my NetSuite clients, who recently went live with Avalara, came to me with an issue related to a lack of permissions. Here's how I fixed it.
Read the Article
Learn how to prevent fraudulent case submissions in SuiteCommerce by removing the Cases tab through customer center role permissions.
Read the Article
Mask sensitive values in NetSuite saved searches with formulas. Securely display only safe details in email notifications.
Read the Article